User Manual

Defining Authorization for Screens and Elements

2/9/26
Defining Authorization for Screens and Elements

Kuika offers flexible and secure authorization solutions for application development processes. Enforcing access control over screens and elements based on user roles enhances your application’s security while ensuring that the right users have access to the right data.

SystemAdmin Role and Permissions

The SystemAdmin role represents users with the highest level of permissions within the application. This role has the following permissions:

  • Access to all screens: Can view and edit all screens in the application.
  • Access to all elements: Can manage all UI components (buttons, input fields, tables, etc.).
  • User and role management: Can create, delete, and change the roles of user accounts.
  • Access to data sources: Can manage database tables and run SQL queries.
  • Modifying authorization settings: Can define user roles and edit authorization policies.
  • Managing application settings: Can change general application configurations.
  • Controlling development and testing processes: Can test how authorizations work in the application’s Preview mode.

Authorization on Elements

1. Role-Based Authorization

On the Kuika platform, users can be associated with specific roles to restrict their access to screens and elements.

1.1. Creating a Role
  1. Log in to the Kuika platform and select your project from the Apps screen.
  2. In the UI Design module, add and select an element from the Elements panel.
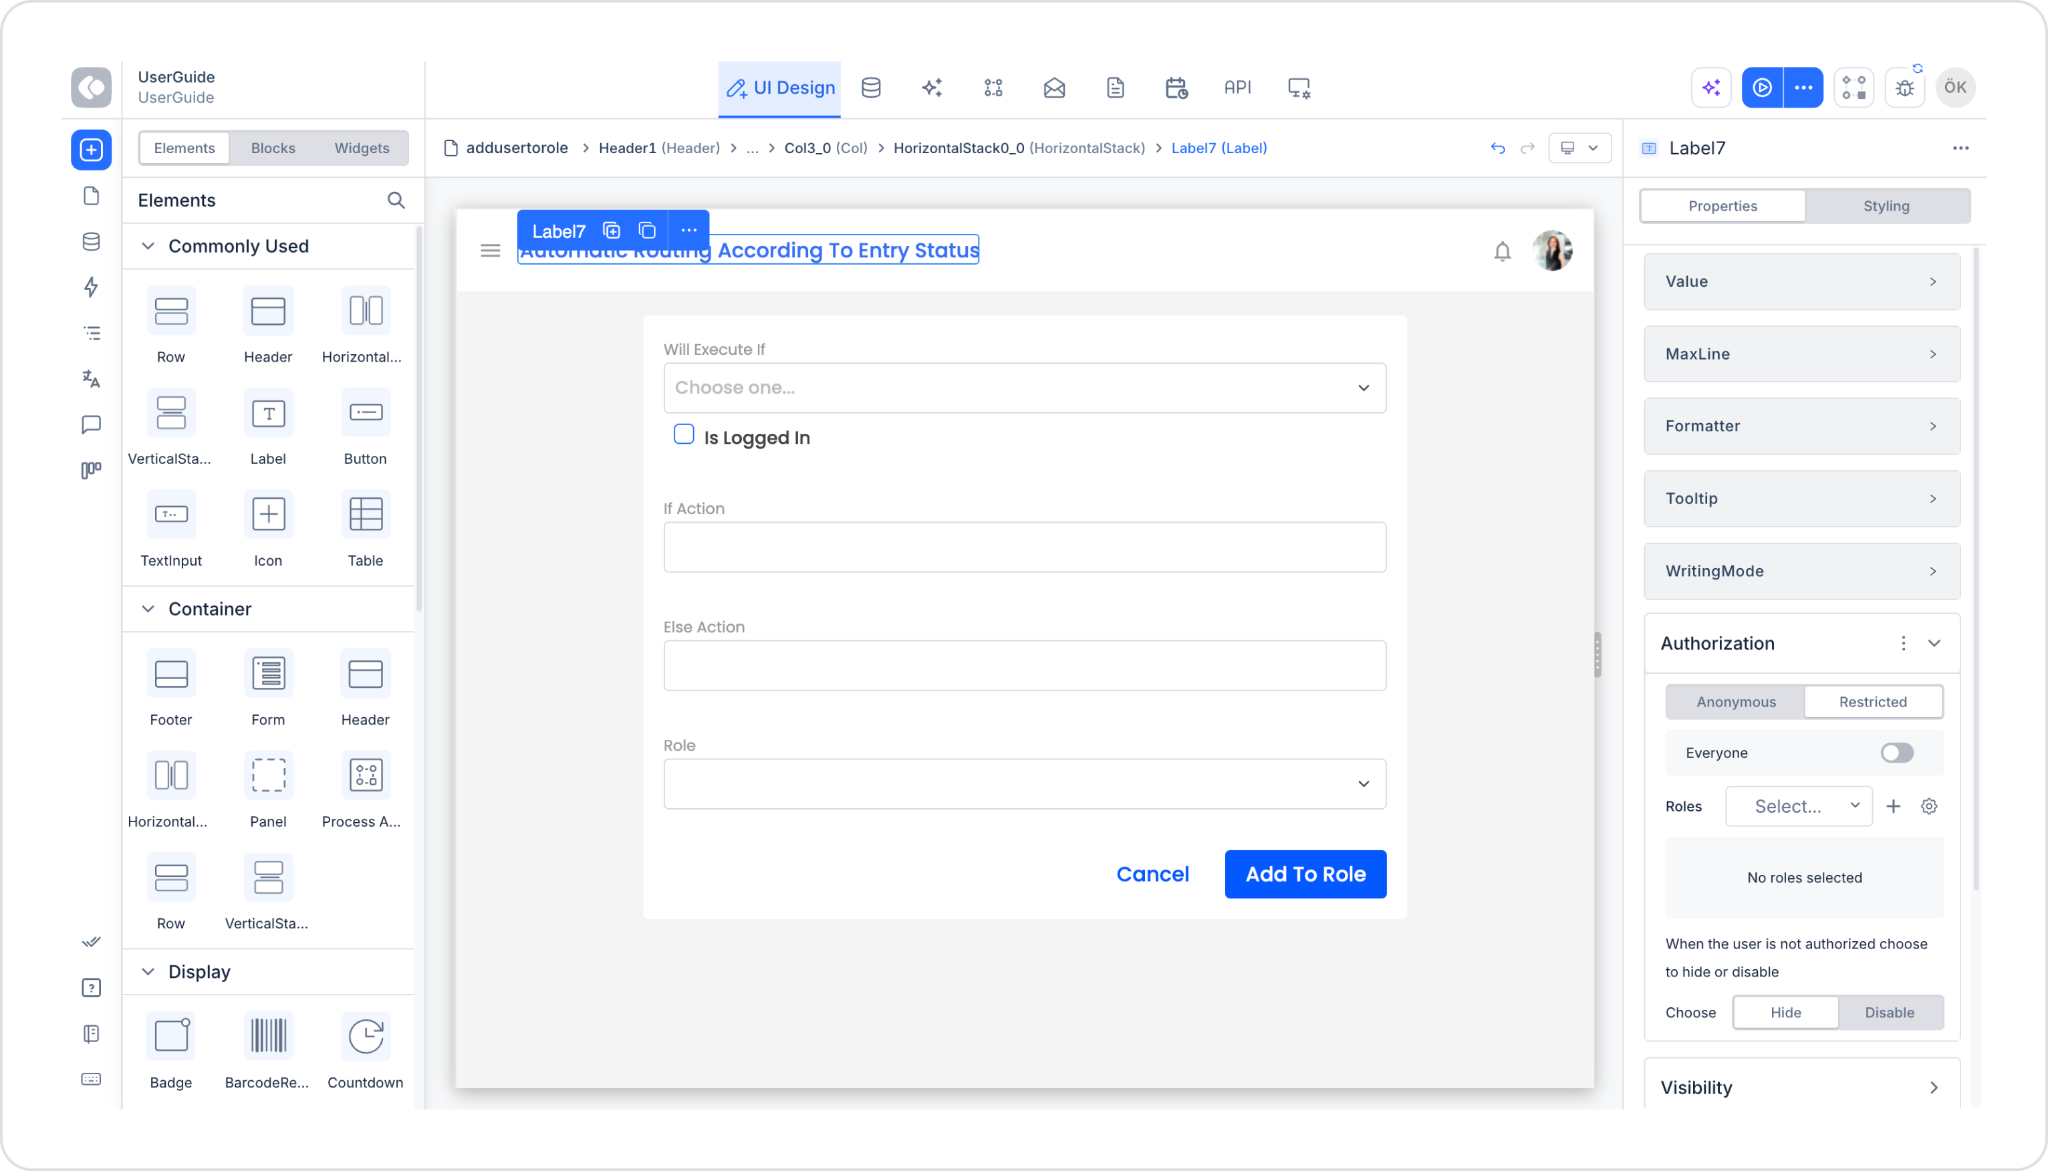
  1. In the Authorization section of the Properties panel, select Restricted from the Anonymous / Restricted options.
  2. Click the + icon next to the Roles heading to open the Role Management modal.
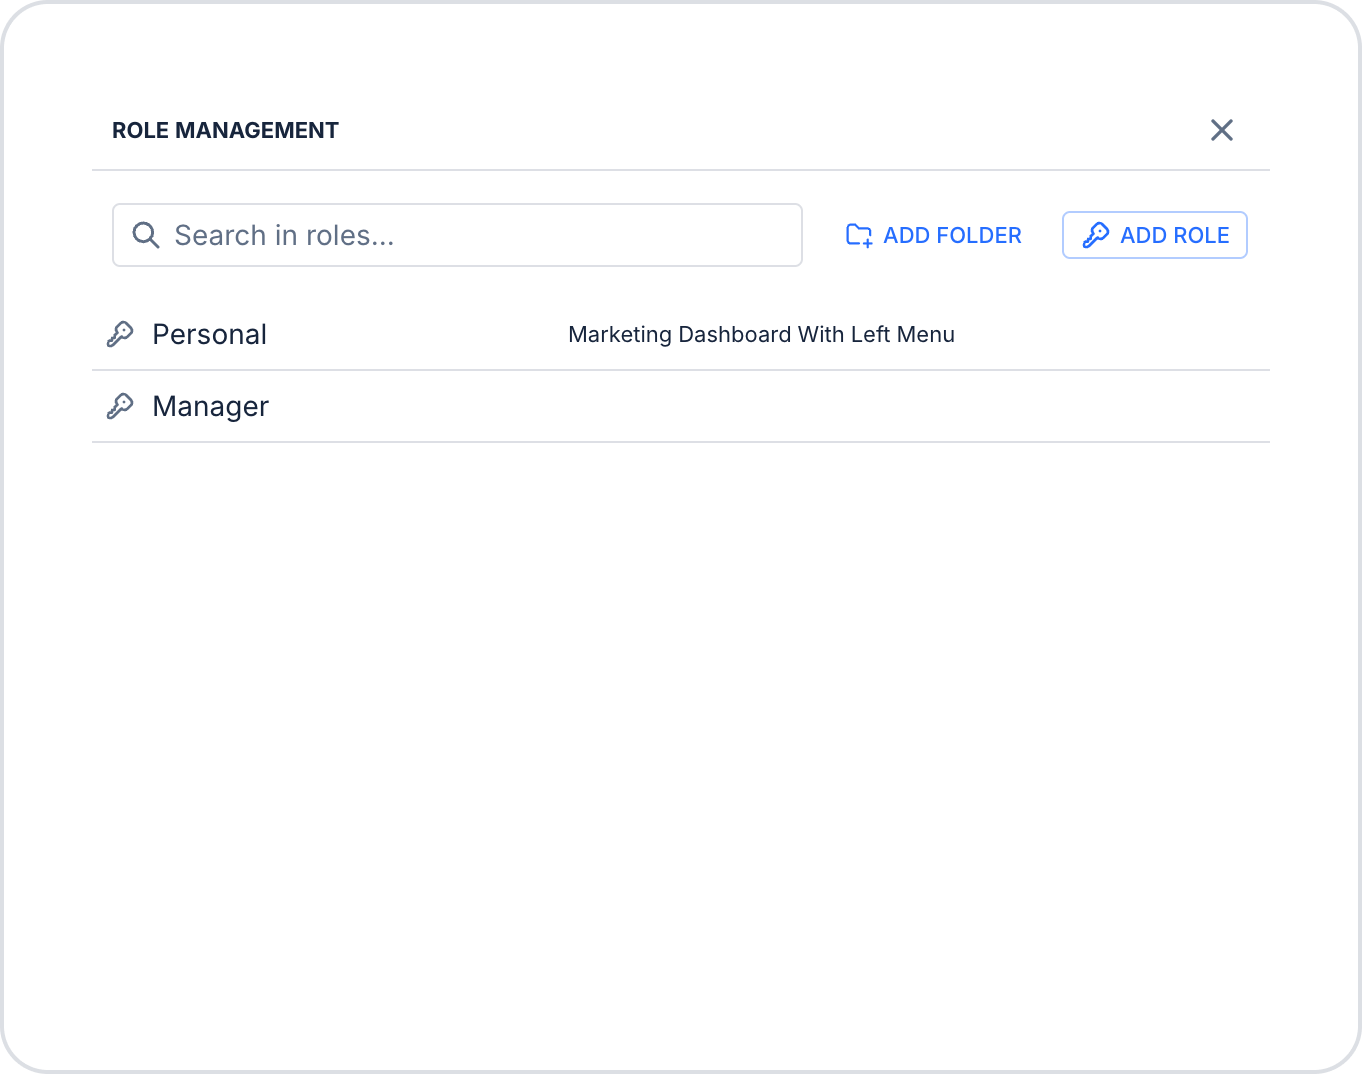
  3. In the modal that opens, you can use the Search in roles... field to search among roles; click the ADD FOLDER button to create a new role group, or the ADD ROLE button to define a new role.
  4. Enter the role name and save to create it.
  5. The roles you create are stored in the KRole table in the Datasources module.
  6. You can write SQL queries using the KUserRole table to determine which roles users have.
A “Clear” icon has been added to the role search field in the Role Management modal. This allows users to clear the text they entered in the search box with a single click, quickly resetting the role list.

1.2. Element Authorization by Role

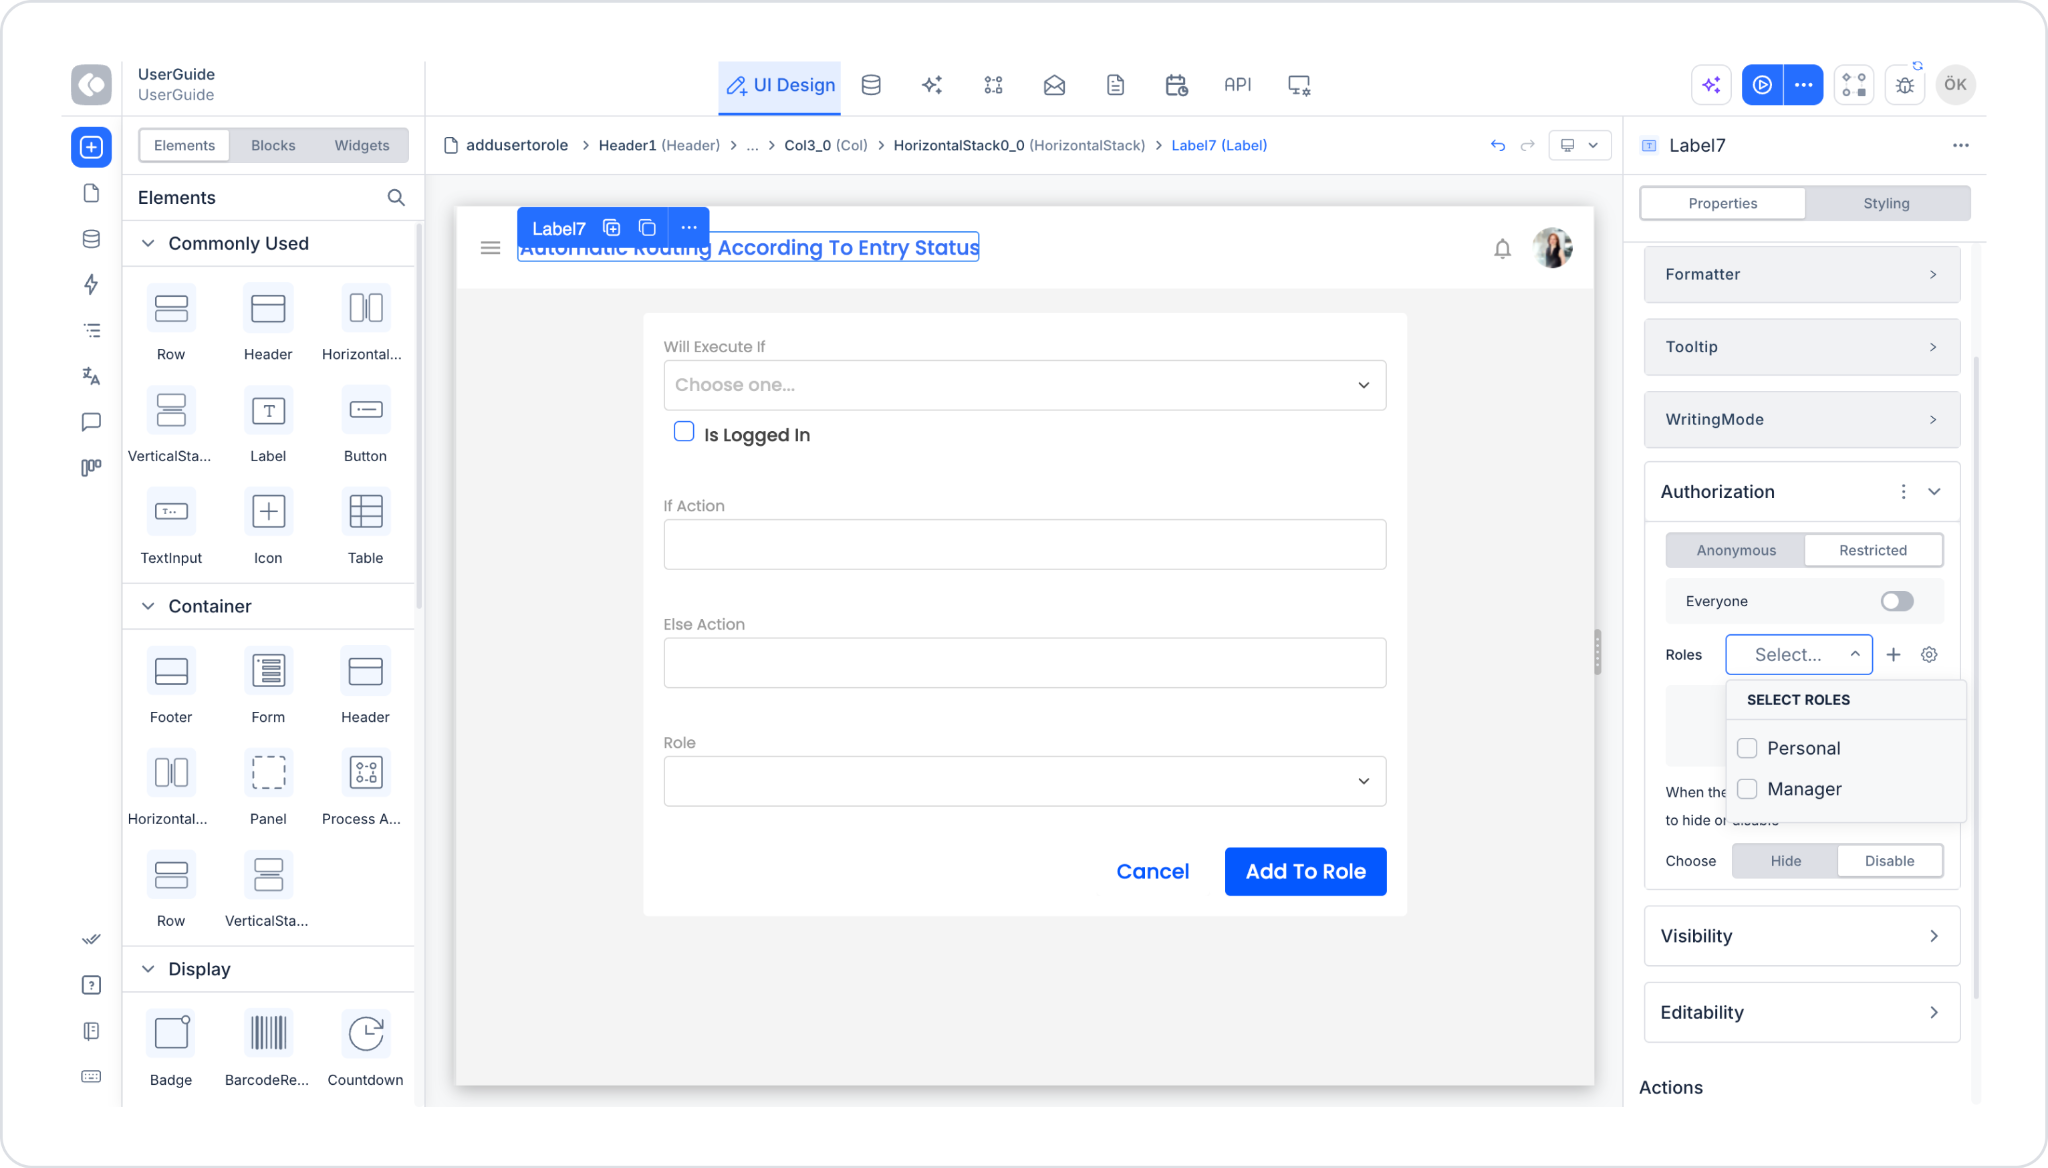
  • To ensure that an element is viewable only by a specific role, check the Restricted option in the Authorization field and select the relevant role(s) (e.g., Personal, Manager) from the SELECT ROLES list via the Select... button in the Roles field. If no roles are selected, the message “No roles selected” appears in the field.
  • If you want all users (regardless of role) to have access, enable the Everyone checkbox.
  • To determine the element’s behavior for unauthorized users, select either the Hide or Disable option under the Choose heading: Hide completely hides the element, while Disable leaves the element visible but inactive (non-interactive).

1.3. Assigning the Start Screen by Role

  • To specify the start screen based on the user’s role, select the role from the corresponding Select dropdown.
  • Click the corresponding save button to complete the configuration.
  • If all roles need to view the same elements, enable the Everyone option.
  • To provide access without requiring a login, you can use the Anonymous option in the Authorization section.

Authorization on Screens

2. Authorization on Screens

Screen-based authorization ensures that users can access only the screens assigned to their designated roles.

2.1. Role-Based Authorization on Screens

  1. Select the screen you want to authorize.
  2. Go to the Authorization field in the Properties panel.
  3. Check the Restricted option and add the relevant role from the Roles field so that the screen can only be viewed by a specific role.

2.2. Authorization in Preview Mode

  • When testing the application in Preview mode, enable the Everyone key so that users can log in.
  • You can use the Anonymous option to allow users to view screens without logging in.

These authorization procedures enhance the application’s security and functionality by ensuring users can access only the areas appropriate for their roles. The SystemAdmin role has the authority to manage all these settings. Thanks to role-based access controls, your application’s user experience and data security can be maximized.

Glossary

No items found.

Alt Başlıklar