User Manual

Authentication Providers

7/10/26
Authentication Providers

In applications you develop with Kuika, you can use the Kuika Auth authentication method by default, or you can customize the authentication process by adding a different Authentication Provider. You can configure these settings through the Kuika Config Manager module.

In this guide, you’ll learn step-by-step how to add LDAP, OAuth 2.0, and Generic Auth (REST) providers as Authentication Providers, as well as how to configure MSAL integration for Microsoft sign-in.
How to Add an Authentication Provider?

1. Open or Create a Configuration

  • Log in to the Kuika platform.
  • From the Apps screen, open the project you’ll be working on.
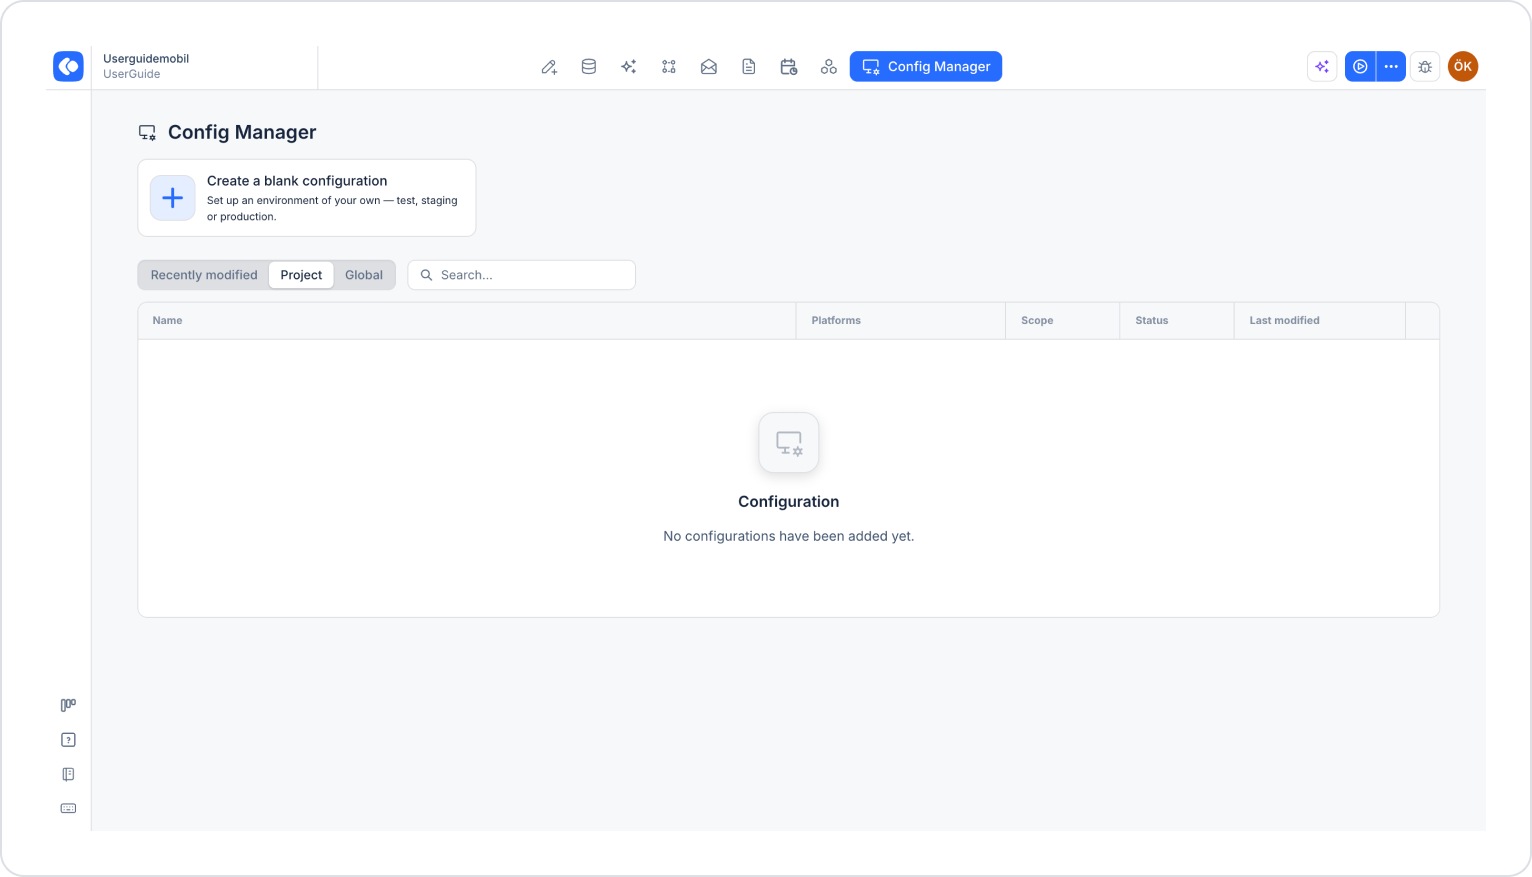
  • Click the Config Manager module in the top menu.
  • To create a new configuration, click the Create a blank configuration card, give the configuration a name, and complete the creation process. If you want to use an existing configuration, click its name in the list.

2. Go to the Authentication & Authorization Settings

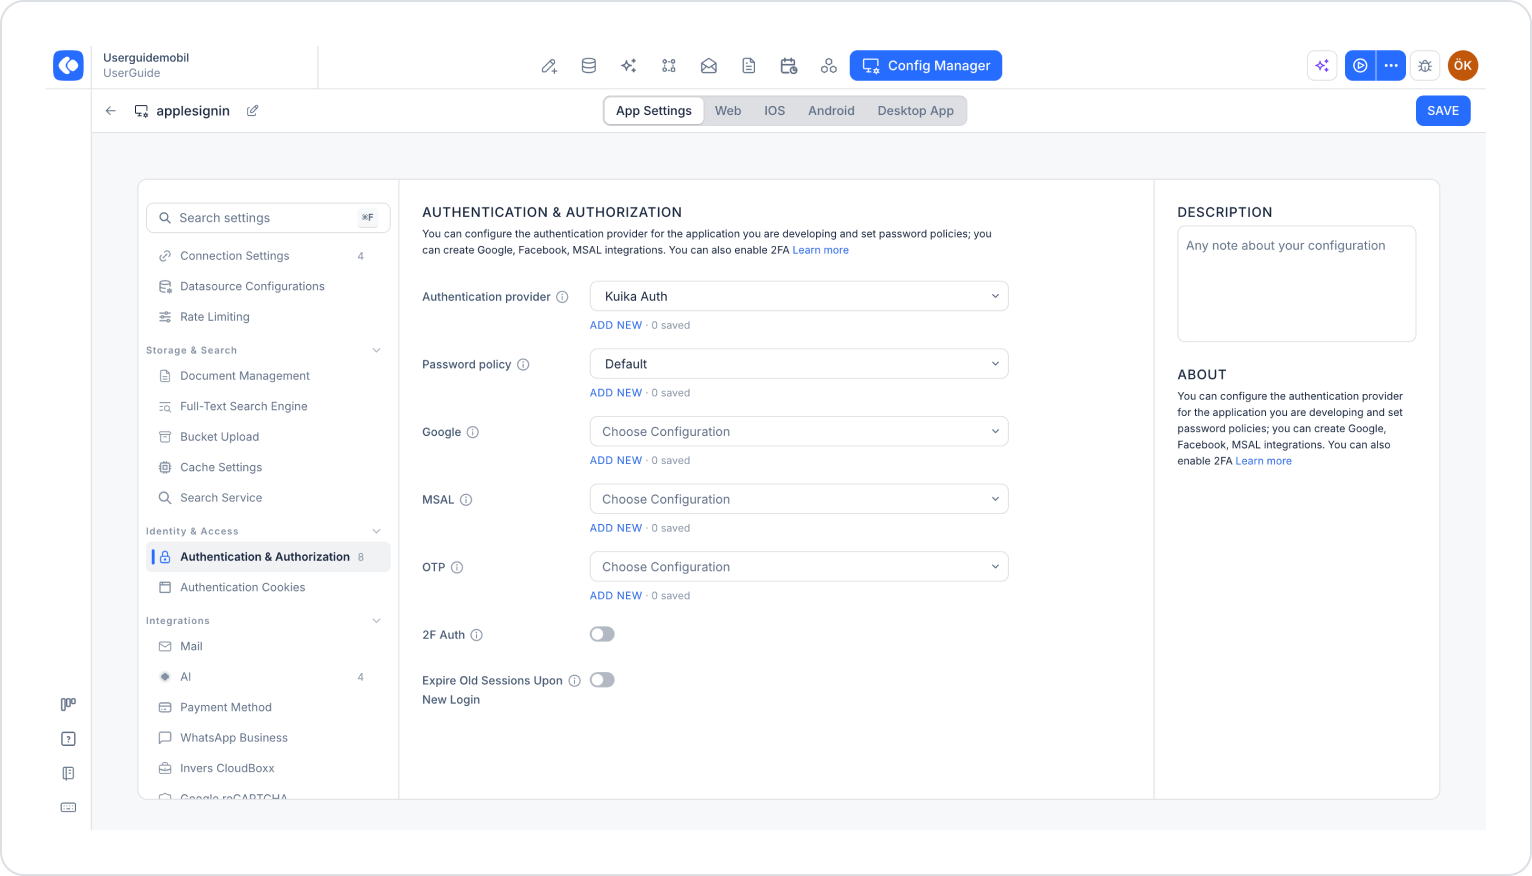
  • Make sure the App Settings tab is selected at the top of the configuration screen.
  • In the left menu, click the Authentication & Authorization option under the Identity & Access heading. You can also quickly access this setting by typing “authentication” into the Search settings field at the top of the menu.
  • Authentication provider is set to Kuika Auth by default. To add a new provider, click the ADD NEW link below the dropdown menu.

3. Select the Provider Type and Fill in the Information

In the Authentication Provider Settings window that opens, select the provider type from the Type (required) dropdown menu:
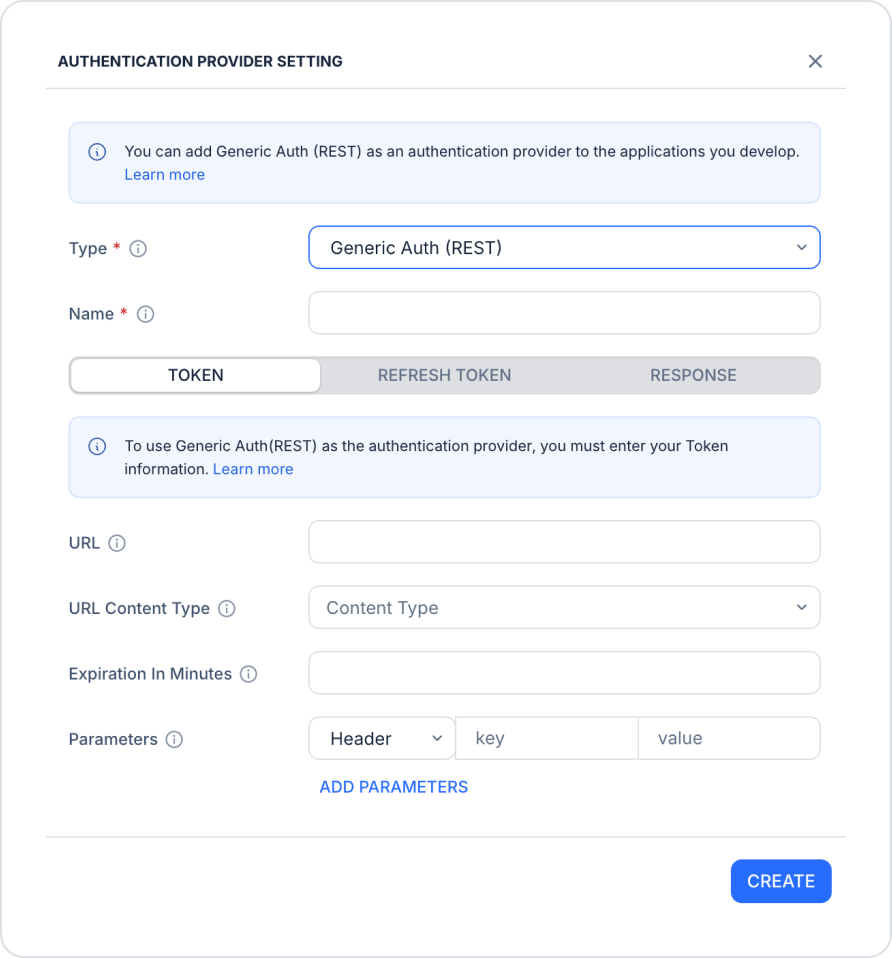
  • Generic Auth (REST)
  • oAuth 2.0
  • LDAP

The fields in the window will change depending on the type you select. For each type, enter a descriptive name for the provider in the Name (required) field, then fill in the fields described in the relevant section below.

LDAP

LDAP (Lightweight Directory Access Protocol) enables secure login to your application by authenticating users defined in Active Directory. Fill in the following fields in the REQUEST section:
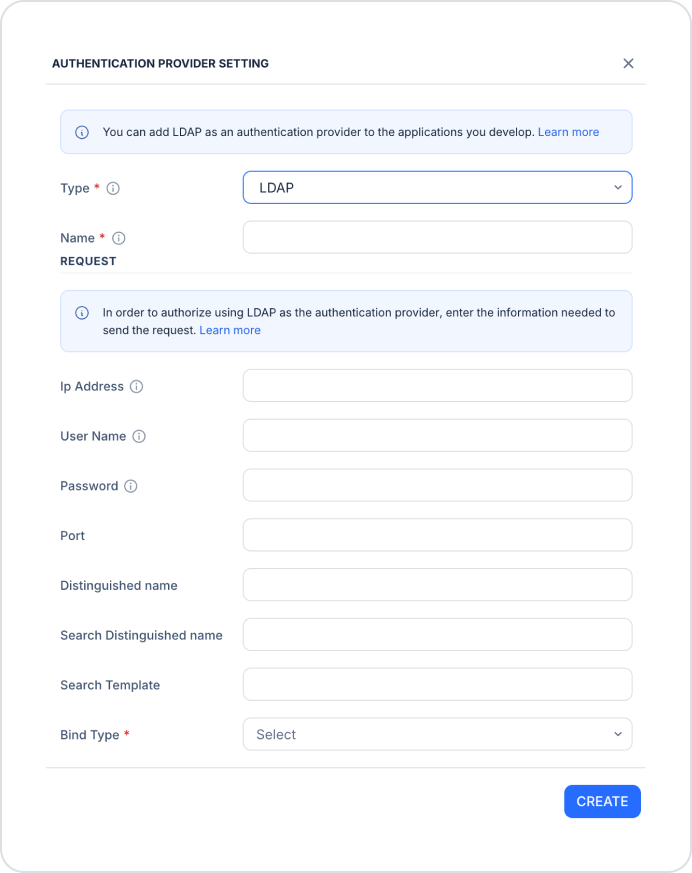
  • IP Address: The IP address of the Active Directory server.
  • User Name: The name of the user authorized to query the directory.
  • Password: This user’s password.
  • Port: The port number to be used for the LDAP connection (typically 389 for LDAP and 636 for LDAPS).
  • Distinguished name: The base directory path to connect to (e.g., DC=example,DC=com).
  • Search Distinguished Name: The directory root where users will be searched.
  • Search Template: User search template (e.g., (sAMAccountName={0})).
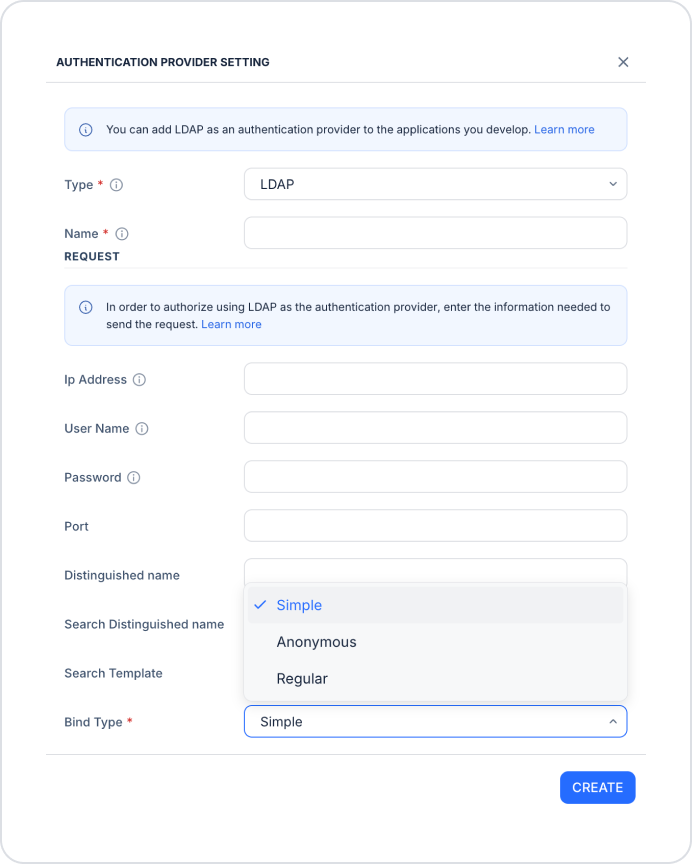
  • Bind Type (required): The type of directory binding. Select one of the following options: Simple, Anonymous, or Regular.

Once LDAP integration is complete, the credentials of users logging into your application are verified through Active Directory.

oAuth 2.0

OAuth 2.0 is an authorization protocol that allows users to securely access an application without sharing their credentials. The window consists of two tabs: REQUEST and RESPONSE.

REQUEST tab
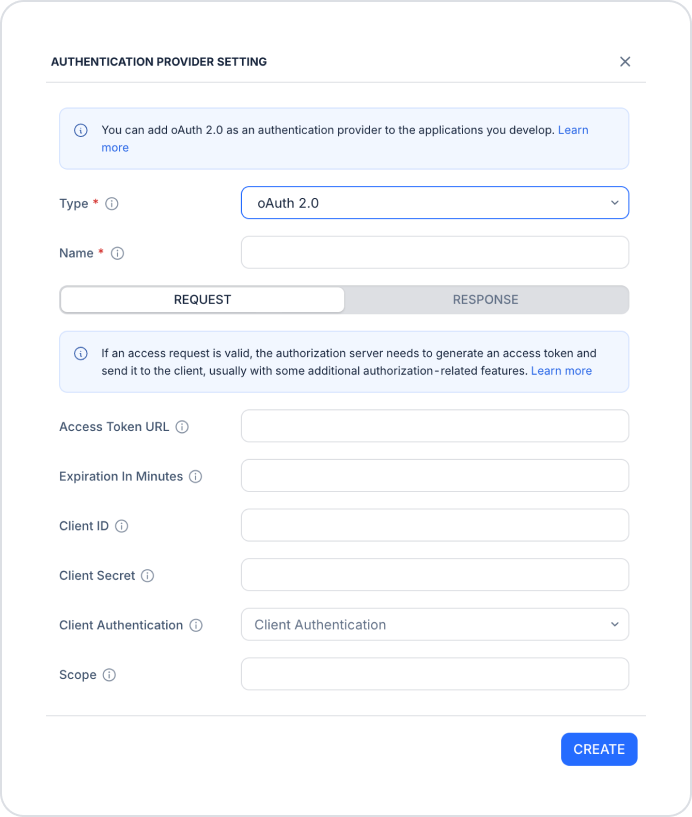
  • Access Token URL: The address to which the request will be sent to obtain an access token.
  • Expiration In Minutes: The token’s validity period (in minutes).
  • Client ID: The client ID provided by your OAuth 2.0 provider.
  • Client Secret: The secret key provided by your OAuth 2.0 provider.
  • Client Authentication: Determines how client information is included in the request.
  • Scope: The access permissions to be requested, if necessary.

RESPONSE tab

In this tab, you map the fields in the JSON response returned by the provider to their equivalents in Kuika:
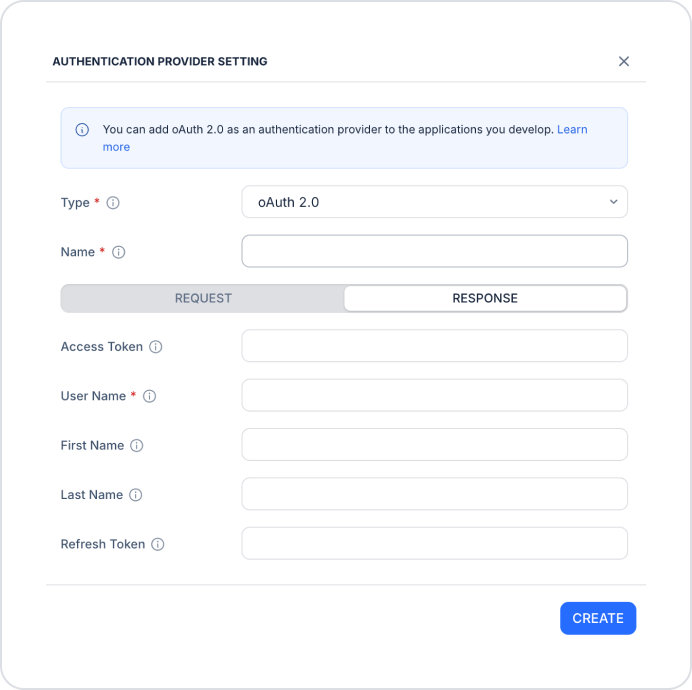
  • Access Token: The access token field in the response.
  • User Name (required): The user name field in the response.
  • First Name: The first name field in the response.
  • Last Name: The last name field in the response.
  • Refresh Token: The refresh token field in the response.

When a Refresh Token is matched in OAuth 2.0, Kuika automatically renews the access token. You do not need to enter a separate Refresh Token URL for this.

Generic Auth (Rest)

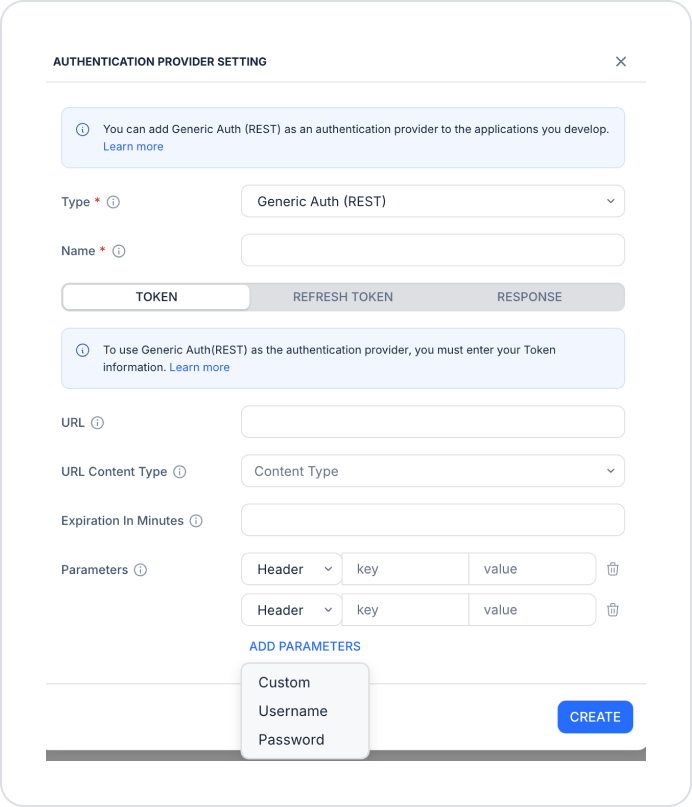
Generic Auth (REST) allows authentication to be performed through your own REST API service. The window consists of three tabs: TOKEN, REFRESH TOKEN, and RESPONSE.

TOKEN tab

  • URL: The address to which the request to obtain a token will be sent.
  • URL Content Type: The data format of the request (e.g., application/json).
  • Expiration In Minutes: The token’s validity period (in minutes).
  • Parameters: Parameters to be sent with the request. Select where the parameter should be added from the dropdown menu on the left (e.g., Header), then fill in the key and value fields.

To add a new parameter, click the ADD PARAMETERS link and select one of the options: Custom, Username, or Password. To delete a parameter you’ve added, click the trash can icon next to it.
REFRESH TOKEN tab

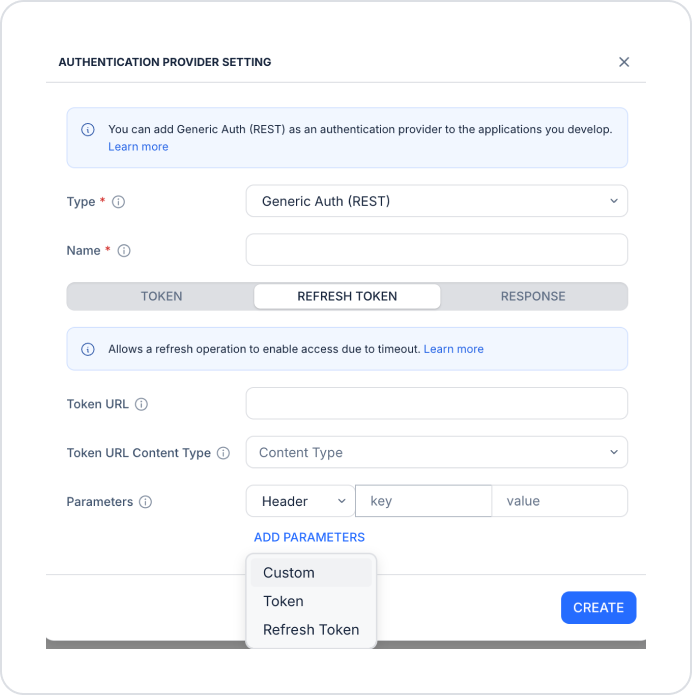
This tab allows you to refresh the token when the session expires.
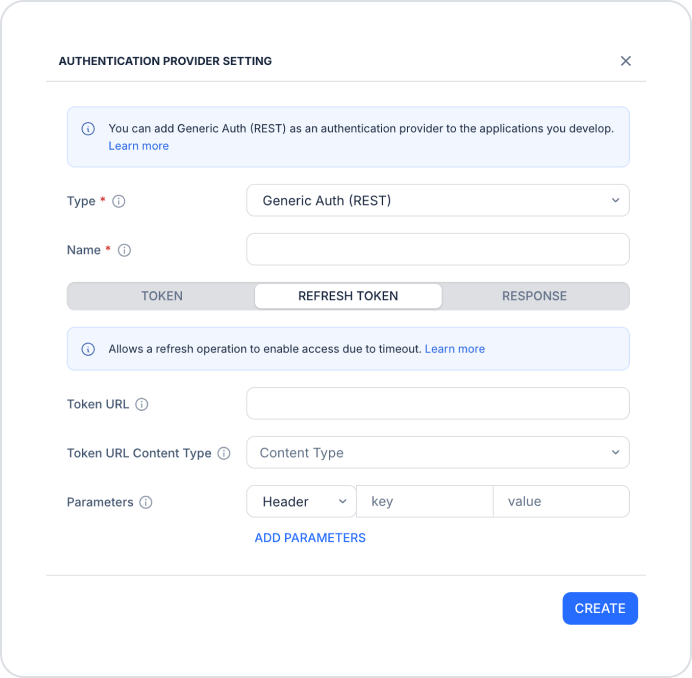
  • Token URL: The address to which the token refresh request will be sent.
  • Token URL Content Type: The data format of the refresh request.
  • Parameters: The parameters to be sent with the refresh request. You can add Custom, Token, or Refresh Token parameters by clicking the ADD PARAMETERS link.

RESPONSE tab

On this tab, you map the fields in the response returned by your service to their corresponding fields in Kuika:
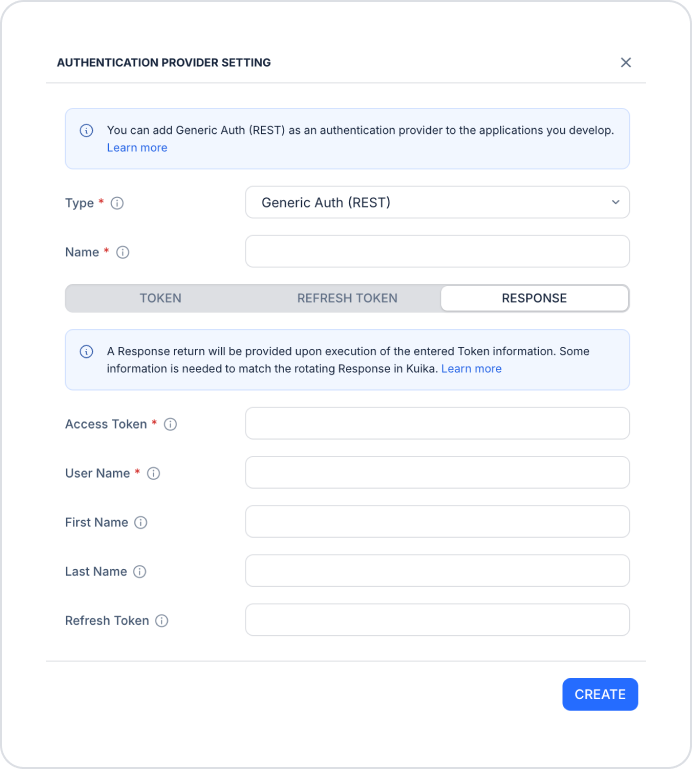
  • Access Token (required): The access token field in the response.
  • User Name (required): The username field in the response.
  • First Name: The first name field in the response.
  • Last Name: The last name field in the response.
  • Refresh Token: The refresh token field in the response.

After entering the information, click the CREATE button to create the provider.

4. Save the Settings

  • Select the provider you created from the Authentication provider dropdown menu.
  • Make sure you’ve filled out all required fields completely and correctly.
  • Click the SAVE button in the top-right corner to save your changes.

Microsoft Authentication Library (MSAL)

MSAL allows your users to sign in to your app using their Microsoft accounts. MSAL is not listed among the Authentication Provider types. It is configured via the separate MSAL section on the Authentication & Authorization screen.

  • On the Authentication & Authorization screen, click the ADD NEW link below the MSAL dropdown menu.
  • In the MSAL Settings window that opens, fill in the following fields:
  • Name (required): A descriptive name for the configuration.
  • Client ID (required): The client ID of your app registered in the Azure Portal.
  • Client Secret (required): The secret key used to authenticate the application.
  • Authority: The authentication URL (e.g., https://login.microsoftonline.com/{tenant}).
  • Scopes: The access permissions to be requested (e.g., user.read).
  • Keystore Base64: The contents of the keystore file in Base64 format.
  • Cache Location: The key that specifies the token cache location.
  • Keystore Hash (Android only): The keystore hash value for Android apps only.

After entering the information, click the CREATE button, select the configuration you created from the MSAL dropdown menu, and click the SAVE button to save it.

Once you’ve completed these steps, you can start using the authentication provider that best suits your needs in your app.

Important Tips

  • Store the Client Secret, password, and token information securely.
  • In response mappings, enter the domain names exactly as they appear in the JSON response returned by your service.
  • Information added in global configurations may appear as read-only or hidden (***) to unauthorized users.
  • Before deploying to production, test the sign-in flow with different users in the test environment.

By correctly configuring the Authentication Provider settings, you can easily integrate your organization’s existing authentication infrastructure into your Kuika applications.

Glossary

No items found.

Alt Başlıklar