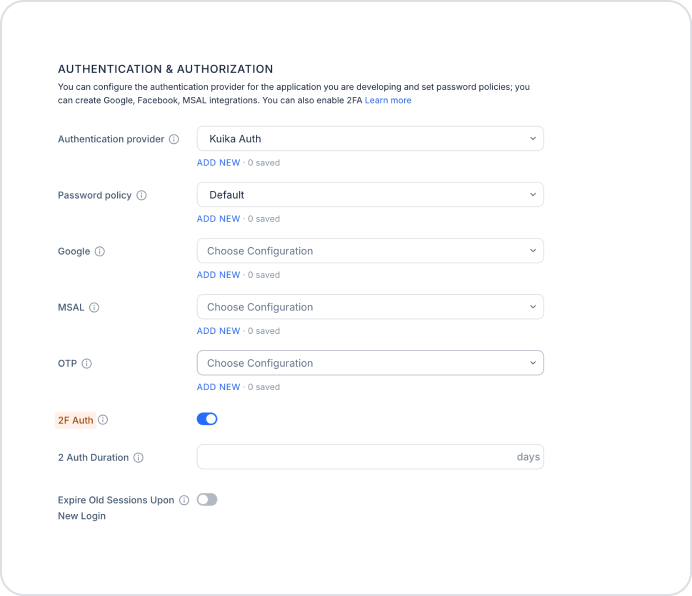
Authentication & Authorization Settings allows you to specify and configure the authentication and authorization methods to be used in your application. By configuring these settings through the Kuika Config Manager module, you can manage the authentication provider, password policies, sign-in integrations with Google and Microsoft (MSAL), as well as OTP and two-factor authentication.
In this guide, you’ll learn step-by-step how to configure authentication settings, how to fill out the required fields for each setting, and how to test the processes.
How to Set Up Authentication & Authorization?
1. Open or Create a Configuration
Log in to the Kuika platform.
From the Apps screen, open the project you’ll be working on.
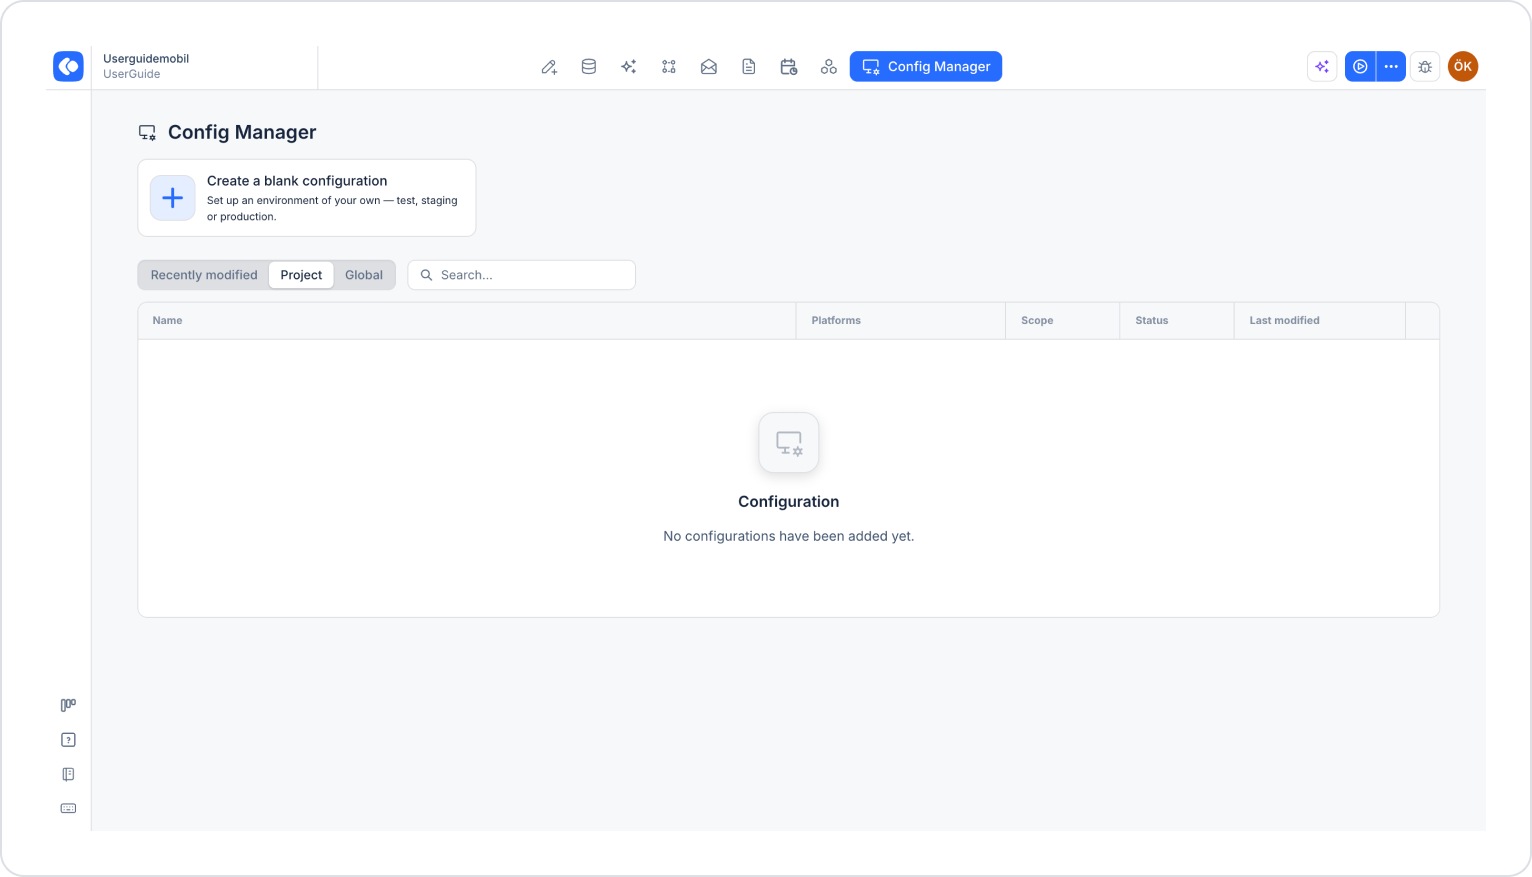
Click the Config Manager module in the top menu.
To create a new configuration, click the Create a blank configuration card, give the configuration a name, and complete the creation process. If you want to use an existing configuration, click its name in the list.
2. Go to the Authentication & Authorization Settings
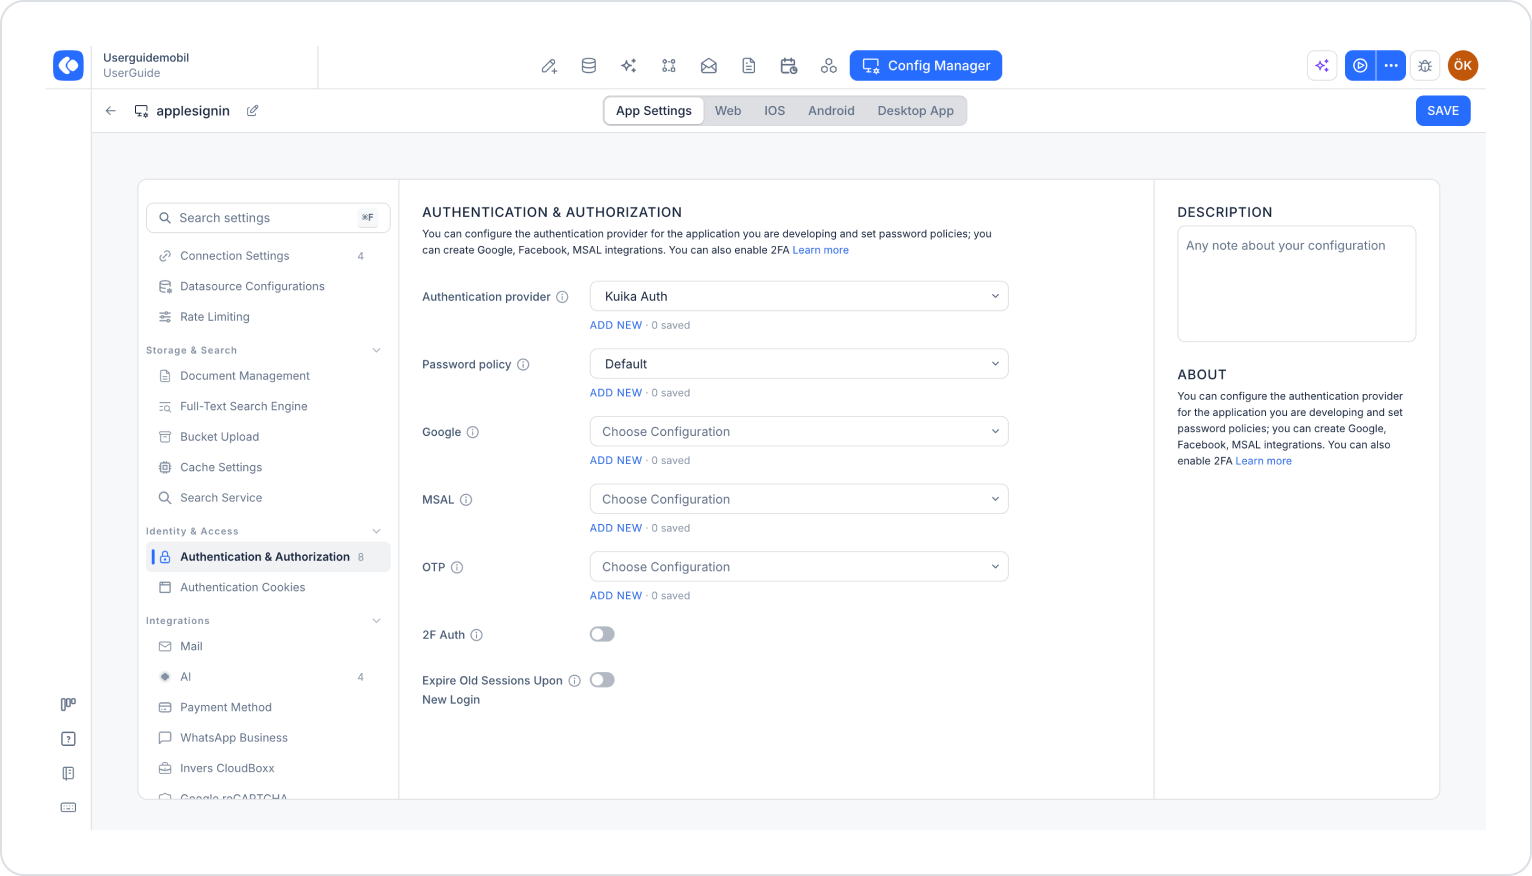
Make sure the App Settings tab is selected at the top of the configuration screen.
In the left menu, click the Authentication & Authorization option under the Identity & Access heading. You can also quickly access this setting by typing “authentication” into the Search settings field at the top of the menu.
The screen contains separate sections for Authentication provider, Password policy, Google, MSAL, and OTP. Click the ADD NEW link under the setting you want to configure.
3. Fill in the Setting Details
Authentication Provider Settings
The authentication provider determines which method will be used for user authentication in your app. By default, Kuika Auth is selected. In the Authentication Provider Setting window that opens, select the provider type from the Type (required) dropdown menu:
Generic Auth (REST): Authentication via a REST service.
oAuth 2.0: Authentication and authorization using the OAuth 2.0 protocol.
LDAP: Authentication via an LDAP directory service.
Password Policy Settings
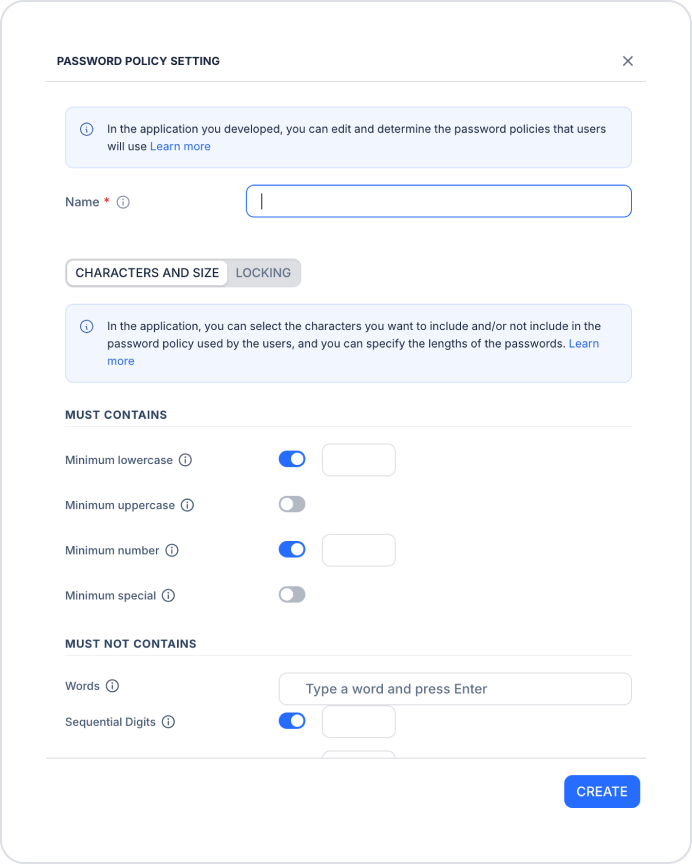
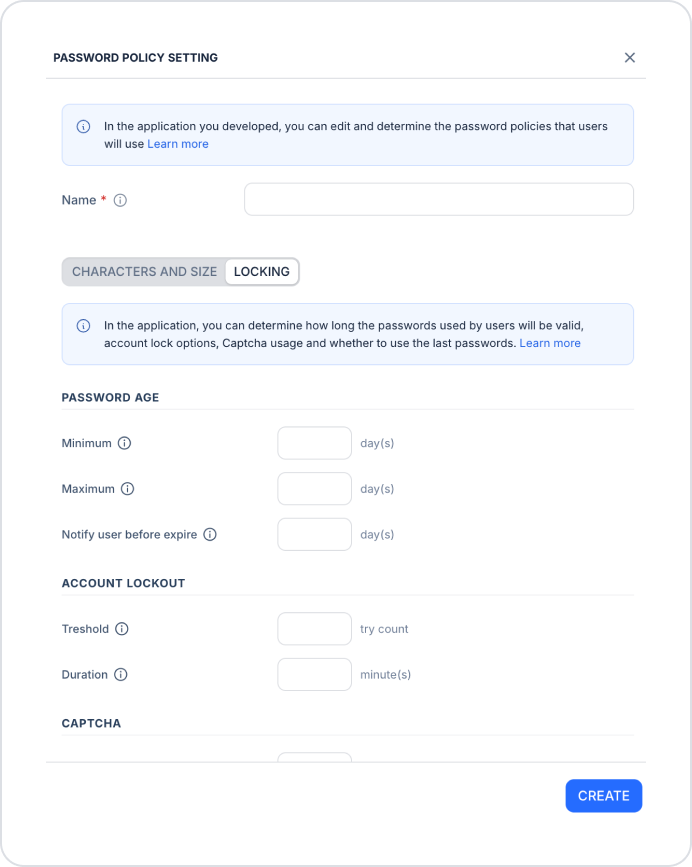
The password policy defines the rules for passwords created by users and account security options. By default, the Default policy is selected. In the Password Policy Setting window that opens, first enter a descriptive name for the policy in the Name (required) field. The window consists of two tabs: CHARACTERS AND SIZE and LOCKING.
CHARACTERS AND SIZE tab
In the MUST CONTAINS section, you specify the characters that must be included in the password. Enable each rule using the toggle and enter the minimum count in the adjacent field:
Minimum lowercase: Minimum number of lowercase letters.
Minimum uppercase: Minimum number of uppercase letters.
Minimum number: Minimum number of digits.
Minimum special: Minimum number of special characters.
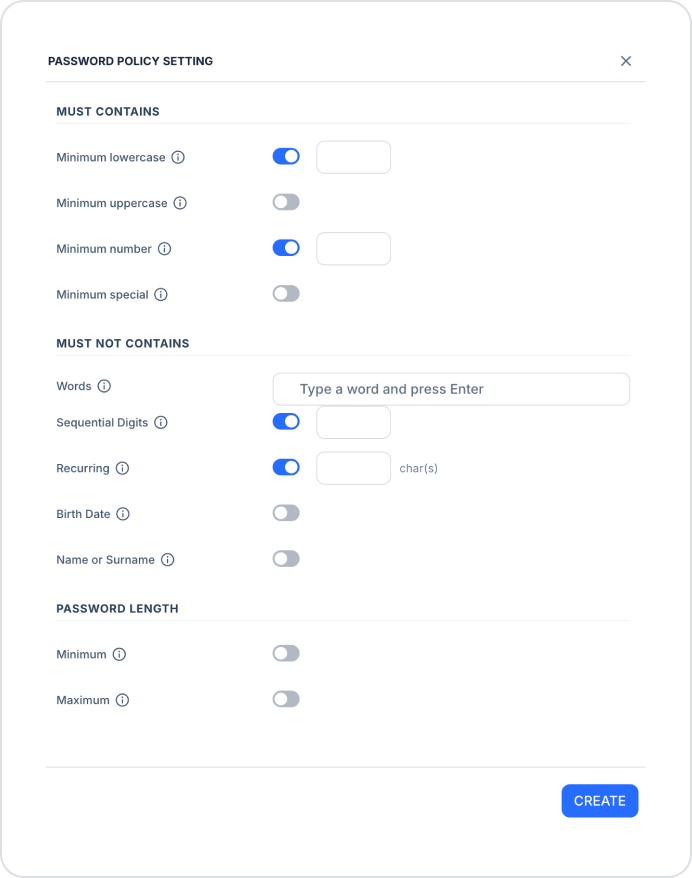
MUST NOT CONTAINS: In this section, you specify the characters that must not be included in the password:
Words: Words you do not want used in the password. Type the word and press Enter to add it.
Sequential Digits: Restricts the use of consecutive digits (e.g., 1234).
Recurring: Restricts the repetition of the same character (by character count).
Birth Date: Prevents the user’s birth date from being used in the password.
Name or Surname: Prevents the user’s first name or last name from being used in the password.
PASSWORD LENGTH: In this section, you set the password length limits:
Minimum: The minimum number of characters in the password.
Maximum: The maximum number of characters in the password.
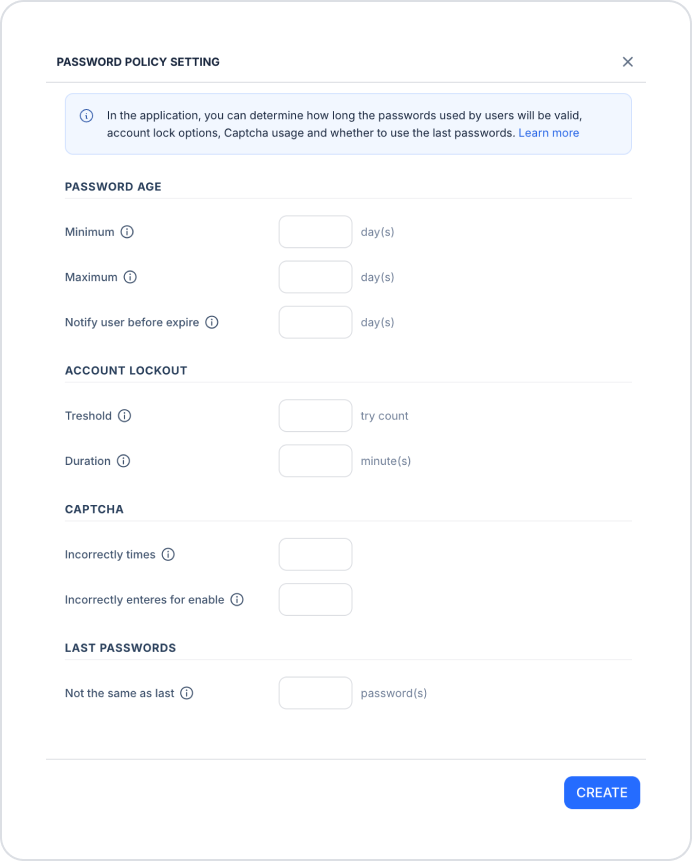
LOCKING tab
In the PASSWORD AGE section, you set the password’s validity period in days:
Minimum: The minimum time that must elapse before the password can be changed.
Maximum: The maximum time the password will remain valid.
Notify user before expire: How many days before the password expires the user will be notified.
ACCOUNT LOCKOUT section: Here, you define account lockout rules:
Threshold: The number of failed login attempts allowed before the account is locked.
Duration: The duration (in minutes) for which the account will remain locked.
CAPTCHA section: Here, you configure CAPTCHA usage to protect against bot attacks:
Incorrect attempts: Setting for the number of incorrect CAPTCHA entries.
Incorrect attempts to enable: The number of incorrect entries required to trigger CAPTCHA.
LAST PASSWORDS section: Here, you limit password repetition:
Not the same as last: The number of previous passwords the new password cannot match.
Google Settings
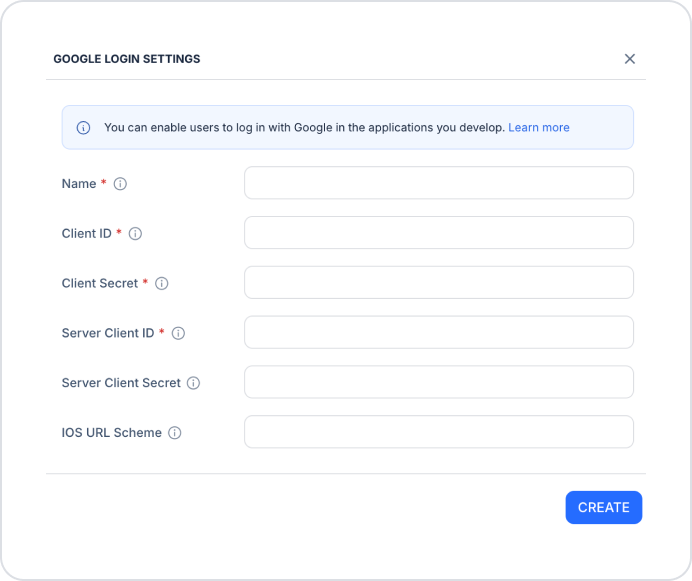
Google Sign-In integration allows your users to sign in to your app using their Google accounts. In the Google Login Settings window that opens, fill in the following fields:
Name (required): A descriptive name for the configuration.
Client ID (required): The client ID provided by Google.
Client Secret (required): The secret key provided by Google.
Server Client ID (required): The server-side client ID.
Server Client Secret: The server-side secret key.
iOS URL Scheme: The URL scheme used for iOS apps.
MSAL Settings
MSAL (Microsoft Authentication Library) allows your users to sign in to your app using their Microsoft accounts. In the MSAL Settings window that opens, fill in the following fields:
Name (required): A descriptive name for the configuration.
Client ID (required): The client ID provided by Microsoft.
Client Secret (required): The secret key provided by Microsoft.
Authority: The authorization URL.
Scopes: The access permissions your app will request.
Keystore Base64: The contents of the keystore file in Base64 format.
Cache Location: The key that specifies the token cache location.
Keystore Hash (Android only): The keystore hash value for Android apps only.
OTP Settings
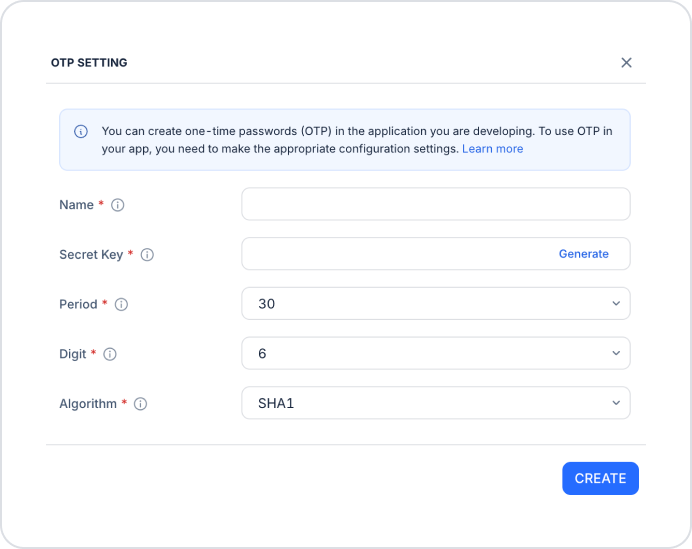
OTP (One-Time Password) enables the generation of one-time passwords for your users. In the OTP Setting window that opens, fill in the following fields (all fields are required):
Name: A descriptive name for the configuration.
Secret Key: The secret key used for OTP generation. You can generate it automatically by clicking the Generate link.
Period: The validity period of the OTP code (default: 30).
Digits: The number of digits in the OTP code (default: 6).
Algorithm: The OTP generation algorithm (default: SHA1).
After entering the information, click the CREATE button in each window to create the configuration.
4. Configure Two-Factor Authentication and Session Settings
2F Auth: Enables or disables two-factor authentication. When enabled, the 2 Auth Duration field appears.
2 Auth Duration: Duration of two-factor authentication (days).
Expire Old Sessions Upon New Login: When enabled, previous sessions are terminated when the user logs in again.
5. Save and Test the Settings
Saving Settings
For each setting you wish to use, select the configuration you created from the corresponding dropdown menu.
Make sure you’ve filled out all required fields completely and correctly.
Click the SAVE button in the top-right corner to save your changes.
Testing
Test user login scenarios with different providers in a test environment.
Test password policy rules, account locking, and CAPTCHA behavior with failed login attempts.
If two-factor authentication is enabled, verify the OTP flow end-to-end.
Once you’ve completed these steps, you’ll have established a secure, multi-layered authentication infrastructure in your application.
Important Tips
Store all sensitive information—such as Client Secret and Secret Key—securely.
Avoid setting password policies that are too strict. Rules that users cannot remember may lead to frequent password reset requests.
Before deploying to production, verify that all authentication providers are configured correctly.
By correctly configuring Authentication & Authorization settings, you can offer your users secure, flexible, and multi-layered access options.