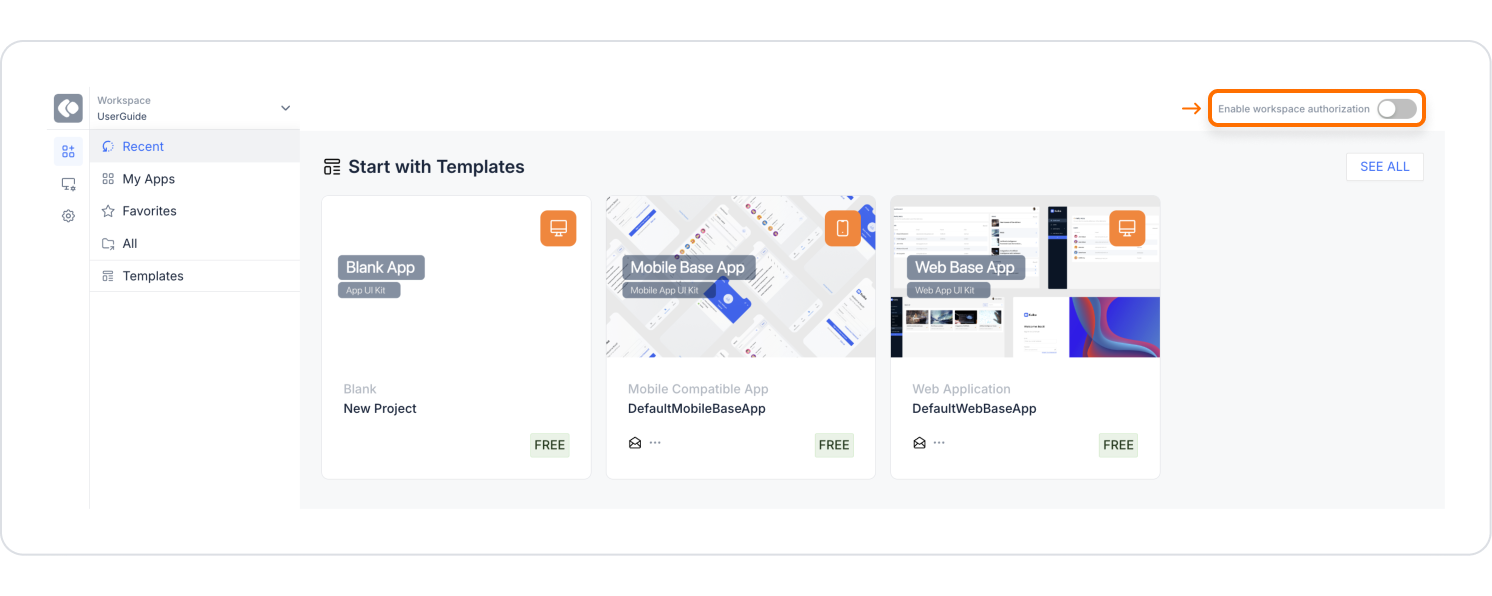
Login to the Kuika platform and go to the Apps screen.
Activate the Enable workspace authorization option in the upper left corner.
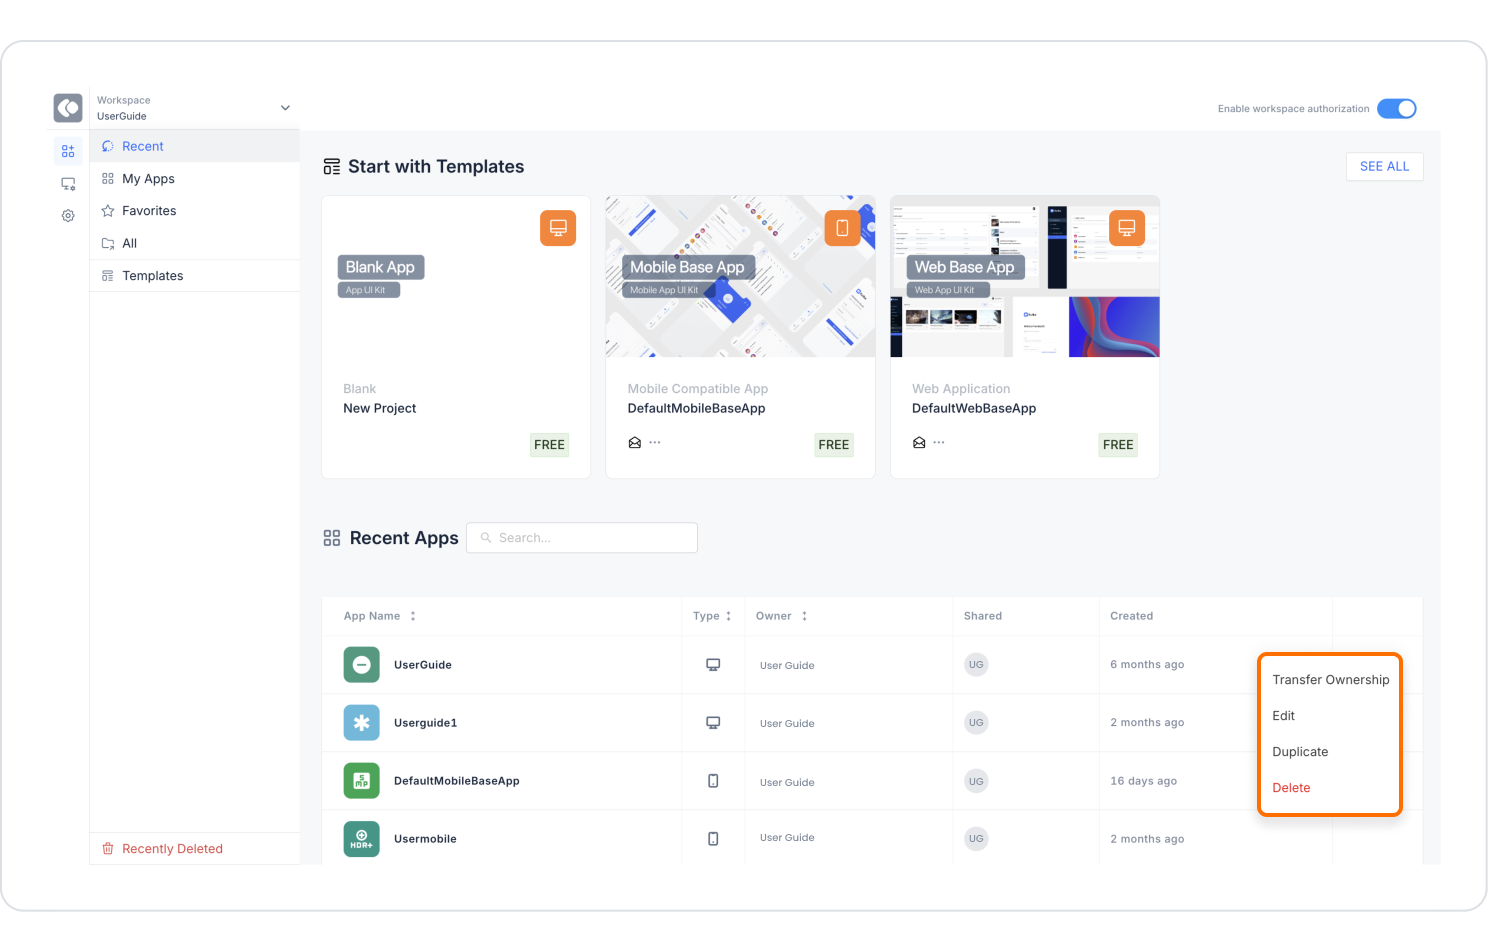
Open the three-dot menu next to the project you want to transfer.
Click on the Transfer Ownership option.
In the pop-up screen that opens, enter the name or e-mail address of the user to whom you will transfer the project.
After specifying the new owner, complete the transfer by clicking the CONFIRM OWNERSHIP TRANSFER button.
By following these steps, you can transfer your projects to the users you want and provide effective management in your workspace.
Transferring Member/Role Relationships When a Project Is Duplicated
When a project is duplicated, the member and role relationships from the source project are automatically transferred to the duplicated project. This eliminates the need to define the user access structure from scratch on the duplicated project; roles defined in the source project—such as Viewer, Developer, and Designer—and the associated users are carried over to the newly created project exactly as they were.
Thanks to this behavior:
User access continuity is ensured after the project is duplicated.
There is no need to manually recreate the authorization structure from the source project.
The roles of members in the copied project can be further edited later via the Share tab, if necessary.
Advanced Authorization with Generated App Roles
With Kuika’s new authorization system, you can now define project-specific Generated App Roles. These roles can contain multiple permission groups and component permissions.
Features:
Invisible in the Designer environment; can only be defined on a project-specific basis.
Follows the Component > Permission Group > Generated App Role hierarchy.
Role creation and editing are performed from the in-app permission management page.
Application Steps:
After adding a user, access can be customized by assigning a Generated App Role.
Each Generated App Role grants permission to view or interact with specific components within the application.
It provides advanced permission control, allowing for personalized access for each user.
Editing User Permissions
User access permissions can be edited in detail using the custom permission management page created within the application.
The user’s assigned Generated App Roles, Permission Groups, and Component Permissions are displayed.
Permissions can be selected from the hierarchical component list.
Role/permission conflicts are checked; changes cannot be made to parent roles without first deleting dependent permissions.
Updates are automatically reflected for the relevant user.
Thanks to these enhancements, project authorization processes on Kuika become much more flexible and customizable. A robust access management infrastructure is established through permission delegation, component-based control, and user-specific access configuration.